CMMC Compliance and Assessment Paths for DoD Contractors
4Cyber helps U.S. defense contractors and subcontractors clarify requirements, evidence, and open actions in a structured way – with the 4Cyber Hub and live group sessions – and build CMMC readiness that holds up.
Which CMMC level and assessment path may apply to a DoD contractor?
CMMC requirements depend on the contract, information in scope, and the level named in the solicitation. Official materials distinguish Level 1 self-assessment, Level 2 self-assessment or C3PAO certification, and Level 3 DCMA DIBCAC assessment. Canadian contracts follow Canadian requirements; Canada may recognize valid CMMC certification case by case after scope review.
CMMC levels at a glance
Which level applies depends on the contract, the information in scope, and the level named in the solicitation. Official materials (32 CFR Part 170) distinguish three assessment paths. 4Cyber supports CMMC Levels 1 to 3: the 4Cyber Hub and live group sessions support your preparation; the assessment itself follows the path your contract requires.
Self-assessment
Level 1 is assessed through a self-assessment by the contractor.
Self-assessment or C3PAO certification
Depending on the contract, Level 2 is assessed through a self-assessment or a certification assessment by a CMMC Third-Party Assessment Organization (C3PAO).
DCMA DIBCAC assessment
Level 3 is assessed by the Defense Contract Management Agency’s Defense Industrial Base Cybersecurity Assessment Center (DCMA DIBCAC).
CMMC Phase I remains in effect – Phase II temporarily suspended
On July 13, 2026, the U.S. Department of War (formerly the Department of Defense) temporarily suspended the external assessment requirements and implementation milestones tied to Phase II. Phase I remains in place. Here is what defense contractors should keep in mind now. Read the official announcement
NIST SP 800-171 Rev. 2 still applies.
During the current transition period, Phase I self-assessments and the contractual safeguarding obligations under DFARS 252.204-7012 remain in place. Keep your readiness, evidence, and open actions current and defensible.
Evidence and documentation requirements remain demanding.
The standard comprises 110 security requirements plus solid evidence such as the System Security Plan and documented controls. Incomplete documentation makes self-assessments – and any government-led assessments – harder.
Phase II is suspended and under review.
The Phase II requirements and the related implementation milestones are currently suspended. How the future external assessment path will look depends on the outcome of the ongoing CMMC review.
What the 4Cyber Hub delivers for CMMC
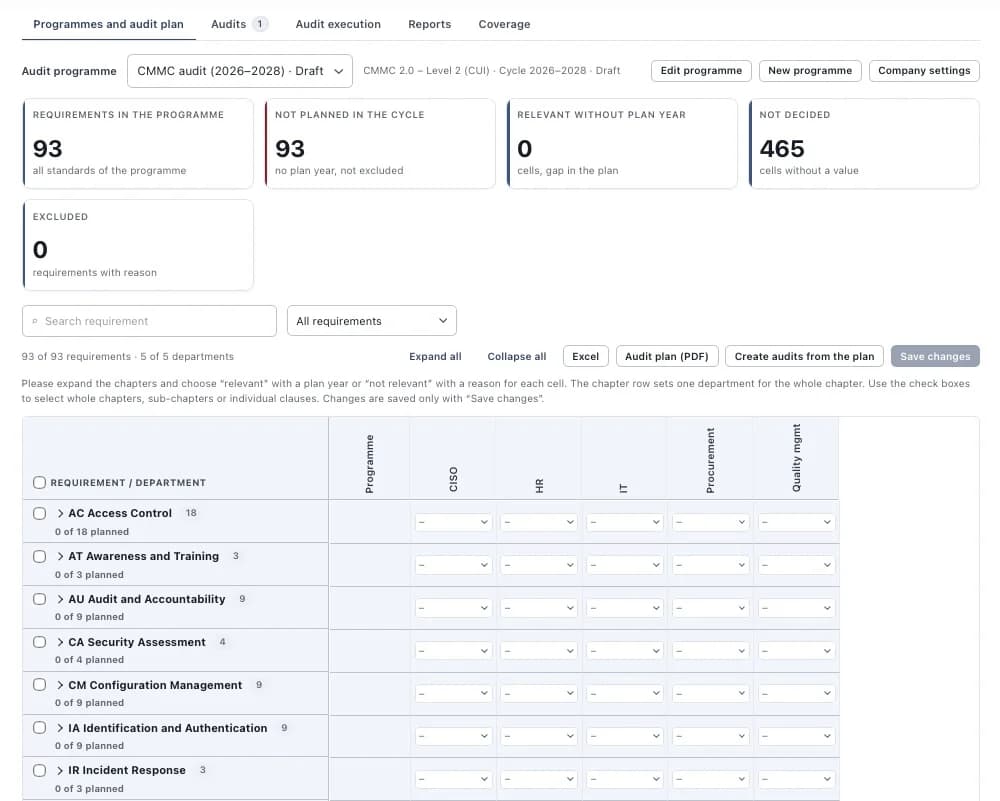
The 4Cyber Hub supports your CMMC readiness with structured control implementation, SSP documentation, task management, and central evidence tracking.
CUI scope & requirements
Capture CUI-relevant areas, systems, and requirements in a structured way – as the foundation for CMMC readiness.
Control implementation
Track NIST SP 800-171 Rev. 2 requirements, controls, and open items in one place.
SSP & documentation
Manage your System Security Plan, policies, and evidence in a structured way and keep them up to date.
Task management
Manage ownership, deadlines, and control status transparently – so implementation stays traceable.
Assessment preparation
Prepare evidence, open items, and assessment questions in one place – for defensible self-assessments and clear internal readiness.
Ongoing compliance
Maintain changes, evidence, and recurring tasks during operations – so readiness and evidence tracking don’t become a one-time project.
From gap analysis to CMMC readiness that holds up
A structured four-step process that takes DoD contractors and subcontractors from scoping and CUI identification through NIST SP 800-171 Rev. 2 to a defensible self-assessment and an evidence structure that is maintained over time. The 25-week 4Cyber program applies to CMMC as well: consulting and implementation support with the 4Cyber Hub, live Q&A group sessions, and special sessions on CMMC. Your assessment result is determined through the assessment path your contract requires.
Scope & CUI identification
- Define system boundaries and CUI data flows
- Review contract and assessment requirements
- Set the project scope and timeline
Gap analysis against NIST SP 800-171 Rev. 2
- Evaluate all 110 security requirements
- Identify and prioritize gaps
- Create your POA&M and SSP
Controls & documentation
- Implement technical and organizational controls
- Finalize the System Security Plan
- Deliver training and awareness
Self-assessment & lasting readiness
- Final assessment against NIST SP 800-171 Rev. 2
- Consolidate evidence for self-assessments
- Prepare for possible future external assessment requirements
In an initial consultation, we clarify where your company stands and which steps make sense.
Who needs CMMC?
CMMC matters for companies in the Defense Industrial Base that handle FCI or CUI under U.S. defense contracts and must meet the related requirements from solicitations, contracts, or the supply chain.
DoD prime contractors
For companies that contract directly with the U.S. Department of Defense and, depending on the contract clause, must meet FCI- or CUI-related security and evidence requirements.
Subcontractors in the DoD supply chain
For companies that receive flowed-down security and evidence requirements from a U.S. defense contract through the supply chain.
Technology & industrial companies
For technology, defense, and industrial companies that want to enter or remain in the U.S. defense market.
Companies with ISO 27001 structures
For companies that want to reuse existing ISMS structures for NIST SP 800-171, self-assessments, and their CMMC readiness.
Use existing ISO 27001 structures for CMMC
Existing ISO 27001 structures can provide a strong foundation for documentation, risk management, policies, responsibilities, and evidence. However, they don’t replace CUI scoping or the contract and evidence requirements specific to CMMC and NIST SP 800-171. The gap analysis shows which content you can reuse.
CMMC in Canada
Canadian defense contracts follow Canadian requirements: Canada has its own cybersecurity certification for defense suppliers (CPCSC), which applies to selected contracts. A valid CMMC certification may be recognized case by case after a scope review. Which requirements apply always depends on the specific contract.
Ready to check your CMMC readiness?
In an initial consultation, we clarify your scope, the relevant contract requirements, and a realistic roadmap for your self-assessment and CMMC readiness.
Frequently asked questions about CMMC
Ready for the next step toward CMMC readiness that holds up?
Start with a clear readiness analysis, a structured action plan, and live group sessions with 4Cyber experts.
No obligation · No sales pressure · A personal assessment of where you stand