ISMS Implementation with 4Cyber Hub and Live Group Support
The 4Cyber Hub guides mid-sized companies from the first gap assessment to a working information security management system – clear, practical, and with live support from experienced experts in group sessions. Certification, if you pursue it, is a separate decision.
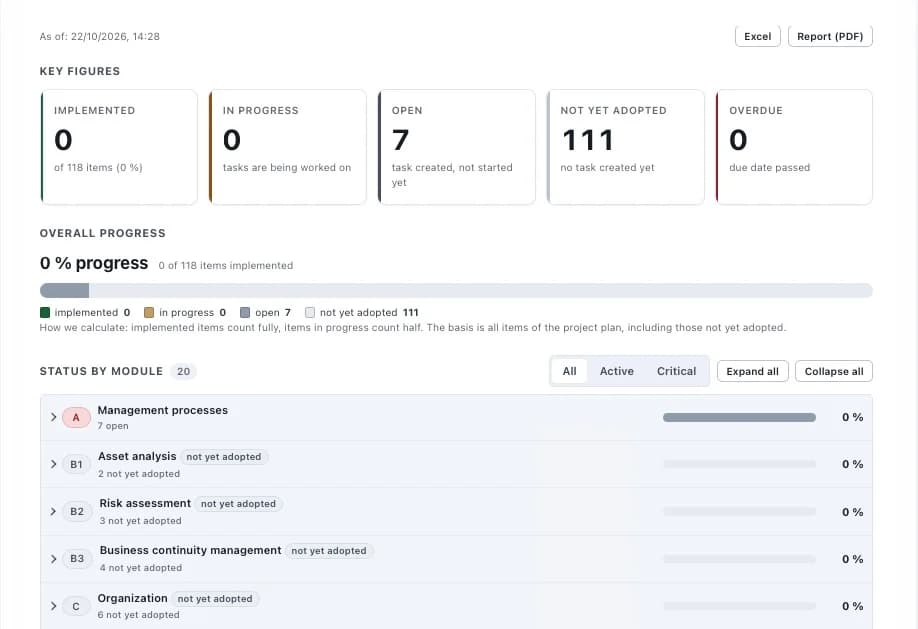
How can an organization implement an ISMS with a tool and live group support?
ISMS implementation defines scope, assesses risk, documents appropriate controls, operates the system, reviews results, and improves over time. The 4Cyber Hub program combines an implementation tool with live group support; certification and framework-specific outcomes remain separate decisions.
Implementing an ISMS isn’t an IT project –
it’s a business decision
Certification alone isn’t the hard part. The real challenge is an ISMS that works day to day, stays up to date, and remains audit-ready.
Compliance has become a business filter.
Customers, supply chains, audits, and bids all demand solid proof. Without a clear ISMS structure, new deals, contract renewals, and customer trust quickly come under pressure.
Time, structure, and expertise are missing in-house.
You know you need it – but ownership, priorities, and capacity are missing. Information security often ends up as a side job for the IT manager or the executive team.
The consultants leave – the work stays.
Traditional projects often deliver a stack of documents. What really matters is an ISMS you can maintain, update, and keep audit-ready over the long term.
What the 4Cyber Hub delivers for your ISMS
The 4Cyber Hub makes ISMS implementation manageable day to day: central documentation, templates, tasks, risk management, learning content, and consulting and implementation support from experts in live Q&A group sessions.
Central ISMS management
Manage scope, roles, tasks, and controls in one place – so your ISMS implementation stays structured and traceable.
Templates & policies
Practical templates, policies, and evidence help you build audit-ready ISMS documentation faster.
Risks & controls
Track risks, controls, and their status in the 4Cyber Hub – so progress, priorities, and open items stay visible.
Learning content & know-how
Guided content and easy-to-follow instructions help your team build security expertise in-house.
Audit readiness in view
Evidence, responsibilities, and updates are maintained continuously – so your ISMS stays audit-ready over time.
Live group sessions
Live Q&A sessions complement the 4Cyber Hub: every topic is explained in detail several times, participants can ask their questions, and special sessions cover individual standards.
What ISMS implementation involves: 25 weeks, step by step
No blank-slate project – a structured roadmap with clear phases, from the first quick check to an ISMS you can run, maintain, and evidence day to day. On your side, a project owner and an internal ISMS project team carry out the implementation; the effort depends heavily on where your company is starting from. By the end, your team can operate the ISMS far more independently – with clear roles, evidence, and routines. The 25 weeks refer to implementing your ISMS; an independent certification audit is a separate step.
Baseline
- Identify gaps and requirements
- Understand your compliance risks
Quick check & analysis
- Gap analysis and prioritization
- Start the asset inventory
Define scope, objectives, and governance
- Define scope and roles
- Set up management processes
Assess risk and select treatment measures
- Implement risk management
- Establish key policies
Document and operate the ISMS
- Train and enable your team
- Manage suppliers and contracts
Monitor, review, and improve
- Internal audit completed
- More independence in running your ISMS
We tailor the roadmap to your company’s scope, maturity, and available internal resources.
Who is our ISMS implementation for?
Our approach is built for mid-sized companies that want to build information security in a structured way, prove they meet requirements, and take pressure off internal teams.
Mid-sized companies without a large security team
For companies that need a structured approach to information security but have limited security resources in-house.
Companies pursuing ISO 27001 or an audit
For organizations that want to become certification-ready or reliably prove they meet customer and audit requirements.
Regulated and security-minded companies
For companies that must translate regulatory or contractual requirements into clear roles, processes, risks, and evidence, and for those that want to strengthen their own security on their own initiative.
Suppliers facing customer security requirements
For suppliers and service providers that must provide security evidence to customers, in bids, or across the supply chain.
Plan the next conversation about your ISMS implementation
In an initial consultation, we review your implementation scope, current documentation, and timeline – and how the 4Cyber Hub and live group sessions fit your situation.
Frequently asked questions about ISMS implementation
Ready for the next step in your ISMS implementation?
Start with a clear roadmap, easy-to-follow implementation steps, and live group sessions with 4Cyber experts.
No obligation · No sales pressure · A personal assessment of where you stand