ISO 27001 Certification Process
The 4Cyber Hub and live group sessions guide you from the first gap analysis to readiness for your certification audit – structured, transparent, and with results you can prove. The certificate itself is issued by an independent, accredited certification body.
What does the ISO/IEC 27001 certification journey involve, and how can an organization prepare without confusing implementation support with independent certification?
ISO/IEC 27001 certification is an optional, independent conformity assessment of an organization’s information security management system against the standard. A practical journey typically defines the ISMS scope, establishes and operates risk-based processes, reviews readiness, and works with an external certification body; the certificate applies only to the stated scope.
ISO 27001 is more than a certificate –
what counts is an ISMS that holds up
The standard itself isn’t the hard part. The challenge is an ISMS that works day to day, stays audit-ready, and keeps running long after certification.
Customers and partners demand proof.
More and more customers, supply chains, and bids require ISO 27001 certification. Without it, new deals and renewals come under pressure.
The road to certification is complex.
Gap analysis, policies, the internal audit, the certification body – there are many steps in between. Without a clear structure, teams quickly lose time, focus, and momentum.
Certification needs ongoing operations.
A certificate only carries weight if the ISMS is maintained, documented, and continually improved.
What the 4Cyber Hub delivers for ISO 27001
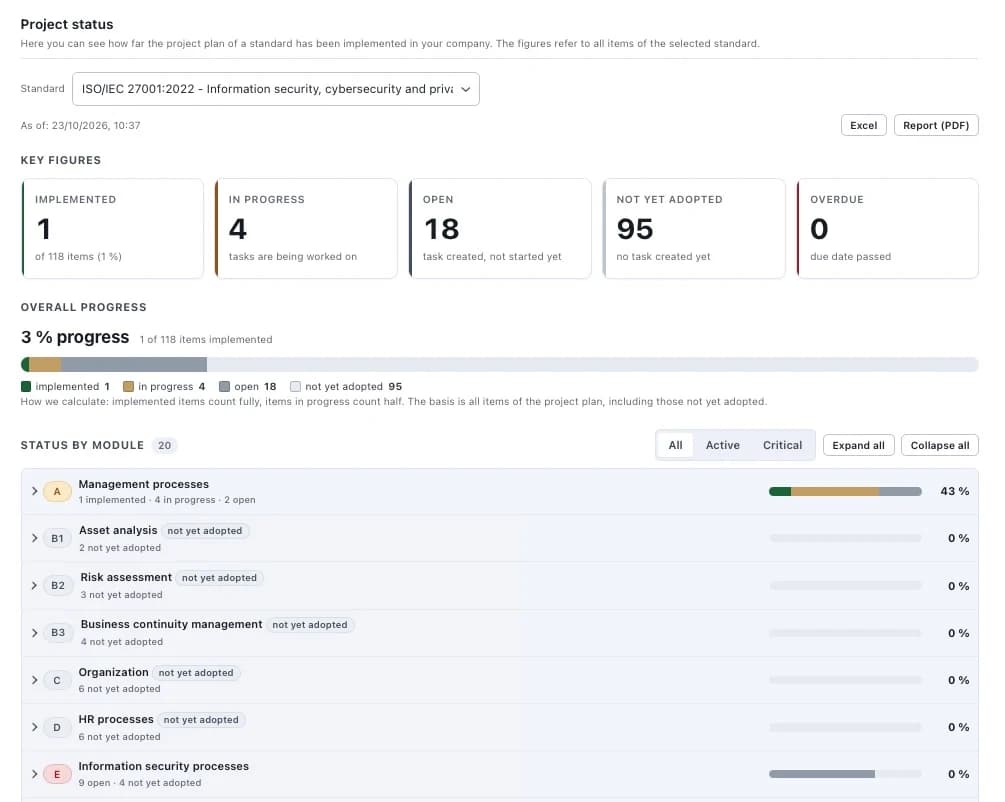
The 4Cyber Hub makes ISO 27001 manageable day to day: central ISMS documentation, tasks, evidence, clear ownership, and structured audit preparation.
Central documentation
Manage ISMS documents, policies, and evidence in one place – structured, versioned, and audit-ready.
Standard requirements & gaps
Map requirements, gaps, and open items transparently – so you always know what’s still missing before certification.
Risks & controls
Manage information security risks, controls, and their status in a traceable way and keep them current during operations.
Tasks & ownership
Assign tasks, roles, and deadlines clearly – so nothing slips through the cracks between audit cycles.
Audit preparation
Prepare evidence, open items, and audit tasks in one place – for internal audits and certification audits.
Ongoing operations
Keep track of updates, management reviews, internal audits, and recertification in a structured way.
The ISO 27001 certification process: from scope to surveillance
A structured five-step process toward ISO 27001 certification – with the goal of an ISO 27001 structure you can run, document, and keep ready for surveillance audits and recertification long after the audit. The 25-week 4Cyber program applies to ISO 27001 as well: consulting and implementation support with the 4Cyber Hub, live Q&A group sessions, and special sessions on ISO 27001. Timing, sampling, and the certification decision belong to the independent certification body.
Define the ISMS scope & assess readiness
- Assessment of your current security controls
- Gap identification against ISO 27001:2022
- Realistic project timeline
Build and operate the management system
- Scope definition and policies
- Annex A controls and risk treatment
- Audit-ready documentation
Conduct the internal audit
- Internal audit based on ISO 19011
- Identification of open items
- Management review preparation
External certification audit (Stage 1 & 2)
- Documentation review (Stage 1)
- On-site audit (Stage 2)
- Preparation in live group sessions
Certificate & ongoing operations
- Certificate issued by the certification body
- Annual surveillance audits
- Recertification after 3 years
You get a prioritized roadmap that reflects your scope, maturity, and available internal resources.
Choose an independent certification body
ISO itself does not certify organizations or issue certificates. Certification is the written assurance of an independent certification body that your ISMS meets the requirements of ISO/IEC 27001 for a defined scope. Accreditation is the formal recognition of a certification body’s competence – ISO recommends evaluating certification bodies and checking their accreditation where relevant.
The 4Cyber Hub and live group sessions support your preparation. The external audit stages, surveillance audits, and the certification decision remain with the independent certification body you choose.
Who benefits from ISO 27001 certification?
Our certification preparation is built for companies that want to prove their information security, win customer trust, and meet regulatory and contractual requirements.
Mid-sized companies facing customer requirements
For companies whose customers require or review ISO 27001 certification.
Suppliers and service providers
For suppliers that must provide security evidence for bids, master service agreements, or supply chains.
Regulated and security-minded companies
For companies that want to meet regulatory or contractual requirements efficiently with an ISO 27001 ISMS, and for those that want to strengthen their own security on their own initiative.
Growing companies & scale-ups
For companies that want to build professional information security early and turn it into a competitive advantage.
How close is your company to certification readiness?
In an initial consultation, we review where you stand, which requirements apply, and a realistic certification roadmap for your company.
Frequently asked questions about ISO 27001 certification
Ready for the next step toward ISO 27001 certification?
Start with a clear ISO 27001 gap analysis, a realistic certification roadmap, and live group sessions with 4Cyber experts.
No obligation · No sales pressure · A personal assessment of where you stand