TISAX Assessment Guidance for
Automotive Suppliers
4Cyber helps automotive suppliers – including U.S. companies that supply German and European automakers – prepare for their TISAX assessment, from ENX registration to sharing the result. The assessment itself is carried out by an ENX-approved audit provider; the 4Cyber Hub and live group sessions support your preparation.
What is a TISAX assessment, and how should an automotive supplier prepare?
TISAX is an automotive-industry information-security assessment and exchange framework governed by the ENX Association. Companies define a scope, prepare against the VDA ISA catalog, choose an approved audit provider, complete the assessment, and share the resulting report or labels through the ENX portal. TISAX labels are not an ISO-like certificate; applicability and assessment objectives depend on partner requirements and scope.
TISAX preparation: where the biggest internal hurdles are
Unclear readiness, a complex VDA ISA and ENX process, and missing routines for keeping the label make structured preparation hard for many suppliers.
Internal readiness often isn’t transparent.
Existing security controls, evidence, and responsibilities are often scattered across teams and documents. That makes it hard to see which VDA ISA gaps really need to be closed before the assessment.
VDA ISA and the ENX process are complex.
Self-assessment, registration, assessment levels, audit providers: the TISAX process has many moving parts that cost time and money if you lack experience.
Keeping your label takes planning.
TISAX labels are valid for a limited time. To keep your evidence usable over the long term, responsibilities, documentation, and follow-up assessments must be prepared in good time.
Why TISAX is business-critical for suppliers
TISAX influences whether suppliers can take part in bids, receive customer approvals, and protect existing supply relationships. What matters is not just the label itself, but its direct impact on market access and revenue opportunities.
Customer approvals & bids
OEMs and Tier 1 customers often require solid TISAX evidence for bids, project approvals, and supplier onboarding.
Market access & supply capability
Missing or unusable TISAX evidence can delay approvals, block new projects, and put existing supply relationships at risk.
Competitive edge in the supply chain
Demonstrable TISAX readiness builds customer trust and can give suppliers an edge over competitors without comparable security evidence.
Preparing for a TISAX assessment with the 4Cyber Hub
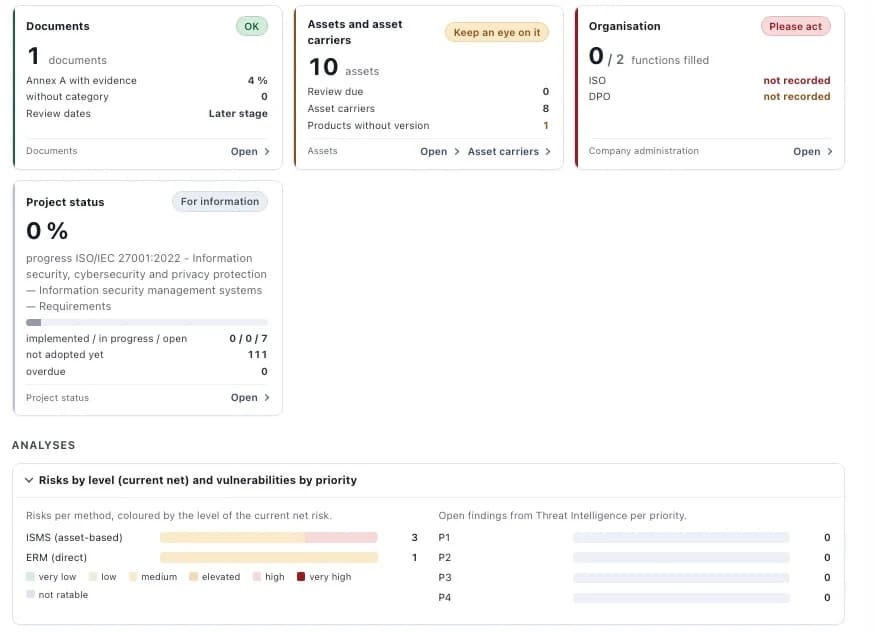
The 4Cyber Hub supports your TISAX preparation with a VDA ISA structure, tasks, evidence, control status, and clear assessment preparation.
VDA ISA structure
Map VDA ISA requirements in a structured way and work through them transparently as you prepare for TISAX.
Scope & requirements
Capture scope, protection needs, and relevant requirements in one place – so your preparation stays focused.
Control status
Track open controls, responsibilities, and progress transparently.
Evidence documentation
Provide policies, processes, and evidence in one place – for your self-assessment and assessment preparation.
Assessment preparation
Manage audit tasks, open items, and evidence in the 4Cyber Hub – so your TISAX preparation stays traceable.
Label maintenance
Keep follow-up assessments, updates, and recurring tasks on track in a structured way.
The TISAX assessment process: from registration to result exchange
A structured five-step process to prepare for your TISAX assessment and then share the result through the ENX portal. The 25-week 4Cyber program applies to TISAX as well: consulting and implementation support with the 4Cyber Hub, live Q&A group sessions, and special sessions on TISAX. The assessment and your TISAX label are the responsibility of the approved audit provider.
Registration in the ENX portal
- Account setup and registration
- Define scope and assessment level
- Select an audit provider
Self-assessment based on VDA ISA
- Evaluate all ISA requirements
- Identify and prioritize gaps
- Create an action plan
Implementation & documentation
- Technical and organizational controls
- Build policies and processes
- Create assessment-ready documentation
Assessment by the audit provider
- On-site or remote assessment
- Preparation in live group sessions
- Evidence and corrections
Labels & result exchange
- Assessment report with TISAX labels
- Share the result with partners in the ENX portal
- Prepare for the follow-up assessment
You get a prioritized overview of the relevant VDA ISA gaps, the required controls, and the next steps toward assessment readiness.
Assessment objectives, labels, and results
Your business partner specifies the assessment objectives that set the benchmark for your assessment. After a passed assessment, the assessment report includes the corresponding TISAX labels. You decide which partners can see your result in the ENX portal.
TISAX labels are not an ISO-like certificate. Which assessment objectives apply depends on your partners’ requirements and your scope.
Who needs a TISAX assessment?
Many German and European automakers require TISAX from their suppliers. Whether you need an assessment depends on your business partners’ requirements, the information you handle, and the assessment scope – it is not a general legal requirement. It typically concerns automotive suppliers – including U.S. companies – that must demonstrate information security to OEMs, for prototype projects, or for sensitive data.
Tier 1 and Tier 2 suppliers
For direct and indirect suppliers in the automotive industry that must meet OEM information security requirements.
Prototypes & development
For companies that work with sensitive vehicle data, prototypes, or confidential design documents.
Companies handling personal data
For suppliers that process personal data of OEM employees and need evidence that it is protected.
Companies already certified to ISO 27001
For companies with an existing ISO 27001 certification that want to reach TISAX efficiently by building on the structures already in place.
TISAX in the supply chain: from customer pressure to a label that holds up
A typical example from the automotive supply chain shows how quickly TISAX turns from a formal customer requirement into a business-critical prerequisite for orders, audits, and supply relationships.
Starting point
A mid-sized automotive supplier is asked by a key Tier 1 customer to provide a TISAX label. Some security controls are already in place, but scope, evidence, responsibilities, and assessment preparation are not yet sufficiently structured.
Challenge
A one-time documentation project isn’t enough if hardly anyone in the company understands the system. Without clear ownership, current evidence, and routines that are actually followed, the same gaps resurface at the next audit or follow-up assessment.
Implementation with 4Cyber
4Cyber supports TISAX readiness, structures the scope and VDA ISA requirements, prioritizes controls, and builds traceable evidence in the 4Cyber Hub. Internal owners are enabled to keep the label secure in day-to-day operations after the assessment.
TISAX and ISO 27001: what can you reuse?
Companies with an existing ISO 27001 structure have a clear head start on TISAX. ISMS documentation, risk management, security policies, responsibilities, audit evidence, and improvement processes can often be reused.
TISAX adds automotive-specific requirements from VDA ISA on top of this foundation – such as prototype protection, information sharing, and assessment levels. TISAX and ISO 27001 remain distinct frameworks: an ISO 27001 certificate does not convert into a TISAX label. Building on existing structures makes TISAX preparation more efficient and keeps your existing evidence usable.
Ready to check your TISAX readiness?
Together we clarify your assessment level, scope, and a realistic timeline to your TISAX label.
Frequently asked questions about the TISAX assessment
Ready for the next step in your TISAX process?
Start with a clear readiness analysis, a realistic timeline, and live group sessions with 4Cyber experts.
No obligation · No sales pressure · A personal assessment of where you stand